
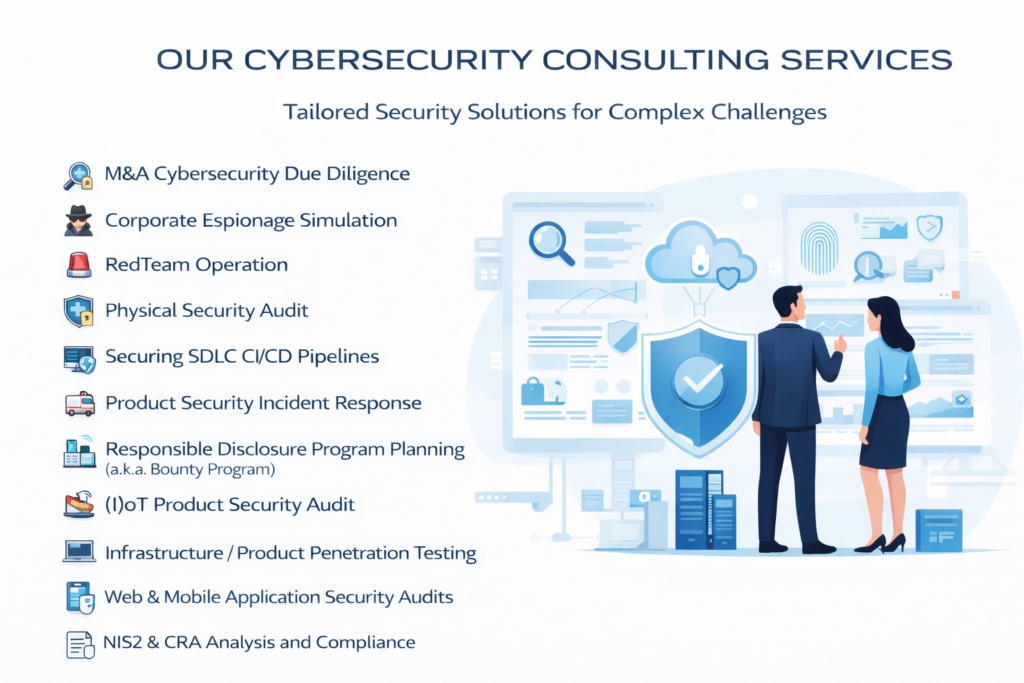
🌐 Web Application Security Audit
Comprehensive security review of web applications, APIs, and backend services, identifying vulnerabilities such as authentication flaws, logic bugs, and data exposure issues.
📱 Mobile Application Security Audit
In-depth security analysis of iOS and Android applications, including reverse engineering, API testing, and backend interaction review to uncover client-side and server-side weaknesses.
📑 NIS2 & CRA Analysis and Compliance
Strategic assessment and technical gap analysis against NIS2 and Cyber Resilience Act requirements, helping organizations and product manufacturers identify compliance risks, define remediation roadmaps, and implement governance, security, and documentation measures aligned with EU regulations.
🔍 M&A Cybersecurity Due Diligence
Independent and confidential assessment of a target company’s cyber risk posture before acquisition, identifying hidden liabilities, historical breaches, insecure architectures, and regulatory exposure that could materially impact valuation.
🕵️ Corporate Espionage Simulation
Realistic simulations of industrial and corporate espionage scenarios to test how well your organization can detect, resist, and respond to insider threats, IP theft, and targeted intelligence-driven attacks.
🚨 Red Team Operation
Full-scope adversary emulation exercises where our experts act as real attackers, combining cyber, physical, and social engineering techniques to evaluate true organizational resilience beyond standard compliance testing.
🔐 Physical Security Audit
Assessment of physical access controls, surveillance, perimeter defenses, and operational procedures to identify weaknesses that could enable unauthorized access, sabotage, or insider abuse.
🧑💻 Securing SDLC & CI/CD Pipelines
Design and hardening of secure development lifecycles and CI/CD pipelines, integrating security controls, code analysis, and supply-chain protections to prevent vulnerabilities from reaching production.
🚑 Product Security Incident Response
Rapid, expert-led response to product or platform security incidents, including vulnerability triage, root-cause analysis, containment, remediation guidance, and executive-level reporting.
🐛 Responsible Disclosure Program Planning (Bug Bounty)
Design and deployment of responsible disclosure or bug bounty programs, including scope definition, researcher engagement rules, legal safeguards, and internal vulnerability handling workflows.
🏭 (II)IoT Product Security Audit
Deep security assessment of IoT and industrial IoT products, covering firmware, hardware, protocols, cloud backends, and supply-chain risks, with a focus on real-world exploitation paths.
🧪 Infrastructure / Product Penetration Testing
Hands-on security testing of networks, systems, and products to identify exploitable vulnerabilities, misconfigurations, and architectural flaws before attackers do.
